

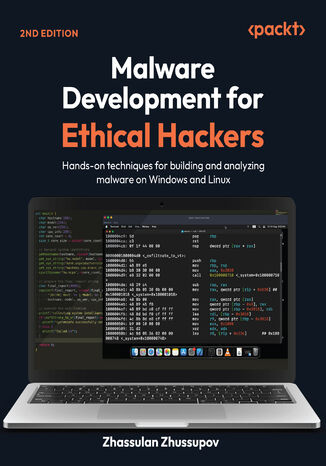
Malware Development for Ethical Hackers. Hands-on techniques for building and analyzing malware on Windows and Linux - Second Edition Zhassulan Zhussupov
 angielski
- Autor:
- Zhassulan Zhussupov
- Wydawnictwo:
- Packt Publishing
- Ocena:
- Stron:
- 258
- Dostępne formaty:
-
PDFePub
Opis
książki
:
Malware Development for Ethical Hackers. Hands-on techniques for building and analyzing malware on Windows and Linux - Second Edition
The second edition covers malware development for Windows and Linux, with hands-on examples in C/C++ and Assembly. You’ll explore execution techniques, evasion, persistence, anti-analysis, abuse of legitimate APIs, low-level system techniques, and real-world tradecraft inspired by modern APTs and malware families. The book also connects offensive development with malware analysis, detection opportunities, and forensic artifacts for security researchers and Blue Team readers.
By the end of this book, you’ll understand how malware is designed, executed, hidden, persisted, and analyzed across Windows and Linux. You’ll be able to build safe lab PoCs, understand adversary behavior, recognize forensic artifacts, and apply this knowledge to ethical hacking, red team simulations, malware research, and practical defense.
Szczegóły książki
- Tytuł oryginału:
- Malware Development for Ethical Hackers. Hands-on techniques for building and analyzing malware on Windows and Linux - Second Edition
- ISBN Ebooka:
- 978-18-074-2758-0, 9781807427580
- Data wydania ebooka :
-
2026-08-31
 Data wydania ebooka często jest dniem wprowadzenia tytułu do sprzedaży i może nie być równoznaczna
z datą wydania książki papierowej. Dodatkowe informacje możesz znaleźć w darmowym fragmencie.
Jeśli masz wątpliwości skontaktuj się z nami [email protected].
- Język publikacji:
- angielski
- Rozmiar pliku Pdf:
- 30MB
- Rozmiar pliku ePub:
- 28.8MB
Dzięki opcji "Druk na żądanie" do sprzedaży wracają tytuły Grupy Helion, które cieszyły sie dużym zainteresowaniem, a których nakład został wyprzedany.
Dla naszych Czytelników wydrukowaliśmy dodatkową pulę egzemplarzy w technice druku cyfrowego.
Co powinieneś wiedzieć o usłudze "Druk na żądanie":
- usługa obejmuje tylko widoczną poniżej listę tytułów, którą na bieżąco aktualizujemy;
- cena książki może być wyższa od początkowej ceny detalicznej, co jest spowodowane kosztami druku cyfrowego (wyższymi niż koszty tradycyjnego druku offsetowego). Obowiązująca cena jest zawsze podawana na stronie WWW książki;
- zawartość książki wraz z dodatkami (płyta CD, DVD) odpowiada jej pierwotnemu wydaniu i jest w pełni komplementarna;
- usługa nie obejmuje książek w kolorze.
Masz pytanie o konkretny tytuł? Napisz do nas: [email protected]
Książka drukowana

Oceny i opinie klientów: Malware Development for Ethical Hackers. Hands-on techniques for building and analyzing malware on Windows and Linux - Second Edition Zhassulan Zhussupov
(0)